Broadcom also joins SE Labs’ new PIVOT programme, as participation in the US-backed MITRE Engenuity evaluations falls from 30 vendors to 11
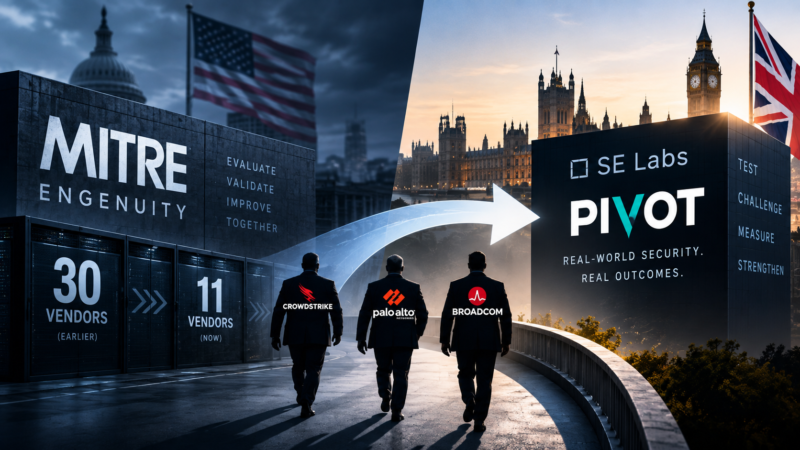
A wave of major cybersecurity vendors is shifting away from the US Department of Defense-backed MITRE Engenuity ATT&CK Evaluations toward a new independent testing programme run by British company SE Labs, according to an announcement made Monday.
CrowdStrike, Palo Alto Networks and Broadcom are among the vendors confirmed for the six-month programme, called PIVOT, SE Labs said. The company said participation in MITRE Engenuity’s evaluations dropped from 30 vendors to just 11 over the past year.
“It’s a landmark moment for British cyber security, as the world’s biggest and best organisations choose to test their critical cyber solutions in the UK rather than in the US,” said Simon Edwards, CEO of SE Labs. “There are now very few tier-one vendors that aren’t testing within PIVOT.”
Edwards said the requirements for cybersecurity testing have changed as attackers adopt new methods, pointing to autonomous AI agent attacks such as the one that affected Hugging Face, and citing the economic impact of the Jaguar Land Rover cyberattack on the UK economy. He said businesses need to know which security solutions can withstand nation-state attacks, major ransomware campaigns and machine-speed threats.
Under PIVOT, teams of ethical hackers from SE Labs will impersonate nation-state hacking groups and other threat actors responsible for major recent breaches, replicating attack types across ransomware, malware and phishing to test vendor products’ ability to detect and defend against known attack groups. The testing phase runs from July to October, with a final report due in January 2027. SE Labs said the resulting data will be shared with analyst firms for independent review before publication, which it said is intended to help vendors identify gaps in their products.
Two of the confirmed vendors framed the programme as a response to demand for verifiable proof of product performance. Adam Bromwich, vice president of engineering and CTO of Broadcom’s Enterprise Security Group, said CISOs today need clarity and proof rather than promises, adding that the programme’s transparency and inclusion of major analyst firms was intended to demonstrate Symantec and Carbon Black’s real-world effectiveness in a verifiable way.
Simon Reed, chief research and scientific officer at Sophos, said the programme would show which vendors are genuinely preventing and detecting threats rather than tuning products to perform well under test conditions, calling the independent assessment critical to maintaining industry trust as the sector shifts focus toward prevention and resilience.
The announcement comes as the UK government develops its Cyber Security & Resilience Bill, which would require designated essential services and digital service providers to report cyber incidents to the regulator and the National Cyber Security Centre within 24 hours, file full reports within 72 hours, widen the scope of regulated sectors, and expand cross-border information-sharing with EU authorities under the NIS2 directive.