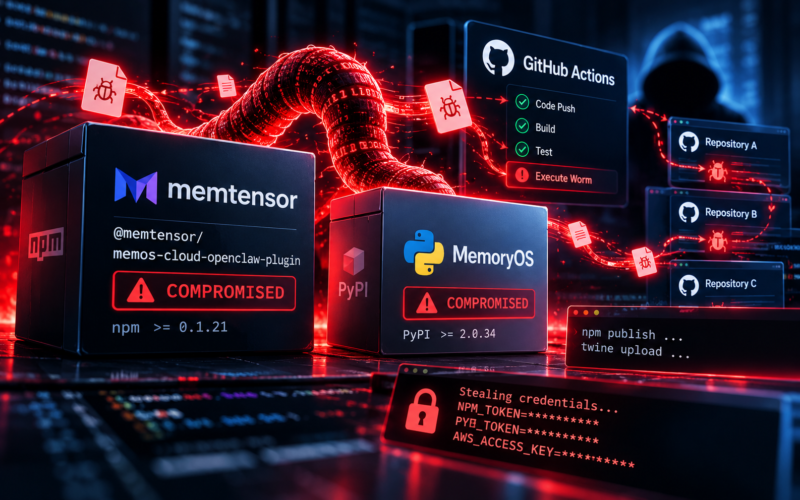
Compromised Memtensor npm plugin spreads worm via GitHub Actions, targets developer credentials
Aikido flags self-propagating malware in trusted packages, with execution shifting from install-time to runtime behavior A compromised npm package linked to Memtensor is being used to distribute a self-propagating supply chain worm capable of spreading across repositories and package registries, according to security firm Aikido. The malware, also identified in a related PyPI package, executes […]
Continue Reading