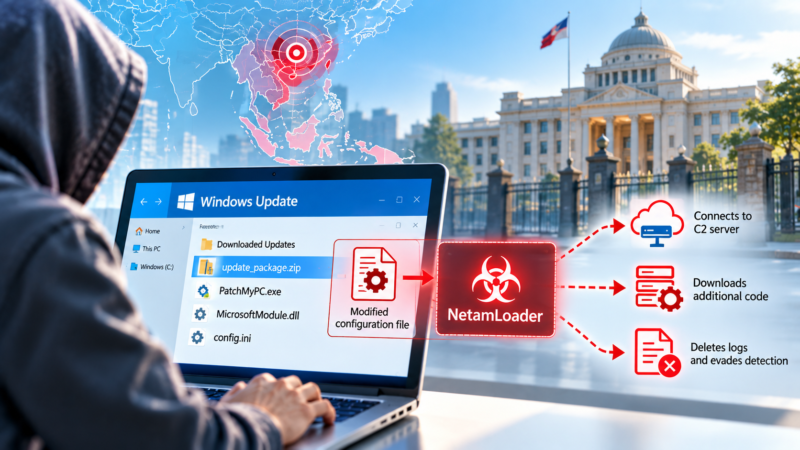
Netamloader-Cyberattack-Targets-Government

Kaspersky uncovers NetamLoader attack targeting government-only Windows system in Asia

Attackers abused legitimate software components to deploy previously unknown malware, manipulate system logs and evade detection on a customized Windows 10 platform. Kaspersky researchers have uncovered an attack targeting a customized version of Windows 10 used exclusively by government organizations in an Asian country, in which attackers abused legitimate software components to deploy a previously […]

Continue Reading
Prince-of-Persia-Cyber-Exfiltration

Iranian espionage group Prince of Persia resurfaces with new command infrastructure, Semperis finds

The group  used US-hosted servers and malware capable of stealing files and routing commands through Telegram, researchers say An Iranian-linked cyberespionage group has rebuilt its command-and-control infrastructure after an unusually long period of inactivity, adopting new hosting arrangements and continuing to use malware designed to steal sensitive files and conduct surveillance, according to research published […]

Continue Reading
PHP2Shell-Global-Cybersecurity-Alert

PHP2Shell flaws put web servers at risk as early exploit attempts emerge

Two critical PHP vulnerabilities allow unauthenticated remote code execution. A disclosure embargo broke down, while security experts warn that AI is making complex exploits more practical. Two critical vulnerabilities in the PHP programming language are drawing urgent attention from security teams after researchers demonstrated unauthenticated remote code execution and Amazon reported an exploitation attempt four […]

Continue Reading
Zeabur-Cloud-Shutdown-Alert

Zeabur to shut down cloud platform after two security breaches expose systemic weaknesses

The cloud deployment provider will begin suspending services on December 1, with a complete shutdown scheduled by year-end, after attackers accessed customer data, credentials and infrastructure in two incidents. Cloud deployment provider Zeabur is winding down its platform after two security incidents in less than two months exposed weaknesses in its infrastructure and credential management, […]

Continue Reading
eMudhra-Certificate-Breach-Alert

eMudhra certificate keys compromised, triggering browser crackdown

Weak private keys could allow attackers to forge trusted certificates and impersonate websites; Google, Mozilla and Cloudflare have taken steps to contain the risk Private keys associated with eight digital certificates issued by Indian certification authority eMudhra have been compromised, according to a Mozilla security engineer, potentially allowing attackers to forge trusted certificates and impersonate […]

Continue Reading
U.S.-Government-DeepSeek-Ban

US orders DeepSeek out of federal IT systems

DHS order extends restrictions to third-party products built using DeepSeek implementations, raising questions about software supply-chain compliance and AI procurement. The US Department of Homeland Security has ordered federal civilian agencies to remove products and services developed by Chinese artificial intelligence startup DeepSeek from their information technology systems, while prohibiting further procurement of the company’s […]

Continue Reading
AI-Phone-Agent-Hijacked-by-Hidden-Prompts

Hidden prompts in texts and emails hijack AI phone agents in half of attacks

Researchers found prompt-based safeguards barely slowed malicious instructions planted in everyday mobile content, a warning for enterprises piloting agents that act on employee devices. AI assistants that operate smartphones can be tricked by fake instructions hidden in everyday messages, emails and calendar invites, a new study has found. On average, the assistants spotted the planted […]

Continue Reading
Red-Hat-Java-Vulnerability

Red Hat says Lightwell fixed 400 Java flaws, but only one CVE is public

IBM and Red Hat’s Lightwell service pairs a $712 million savings model with embargoed fixes for paying customers. Security teams still have little public data to verify the claims More than 400 previously unknown vulnerabilities in widely used Java libraries have been fixed through a new IBM and Red Hat remediation service. Only one of […]

Continue Reading
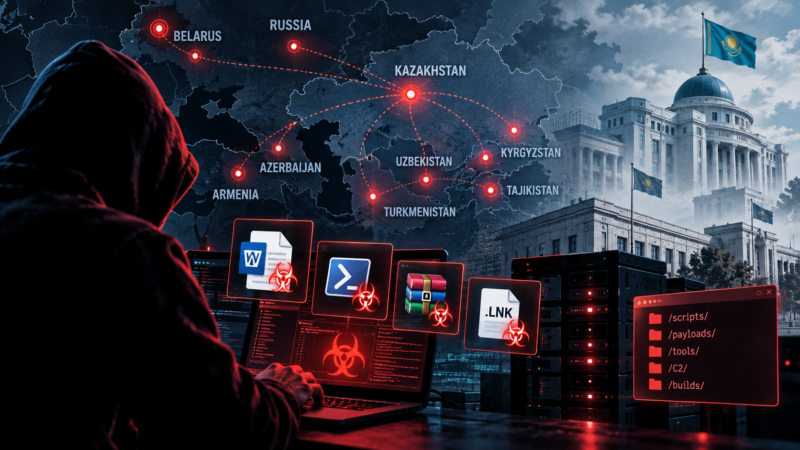
Cyberattack-Map_-Hacker-Threat

Hackers target government organizations in nine CIS countries

Cisco Talos and Recorded Future identified four malware delivery methods and exposed infrastructure linked to the campaign, which researchers assess may have a Kazakhstan connection. A threat group targeting government organizations across Central Asia and the Commonwealth of Independent States (CIS) has used four different methods to deliver malware, including a WinRAR vulnerability exploit, while […]

Continue Reading
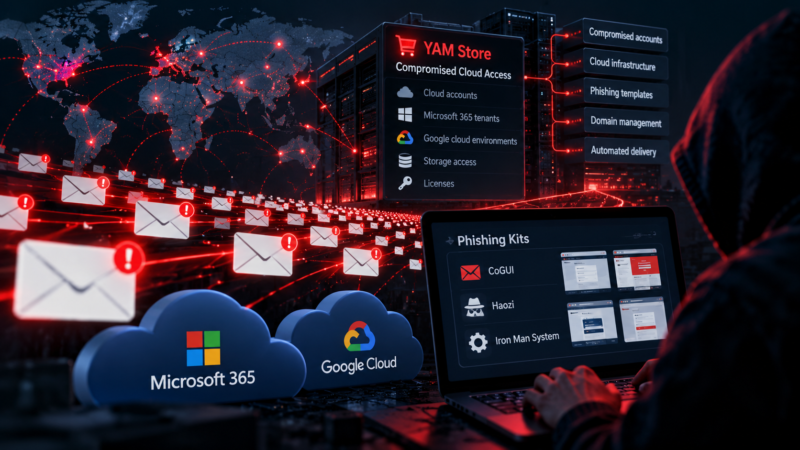
microsoft-yam-store

Microsoft uncovers phishing network behind 1 billion messages

The ecosystem combines phishing kits with an underground marketplace selling compromised cloud environments, enabling attacks against organizations in more than 150 countries. Microsoft has uncovered a cybercrime supply chain that combines phishing-as-a-service kits with an underground marketplace selling compromised cloud environments, enabling criminals to send more than one billion phishing emails and SMS messages to […]

Continue Reading