memtensor

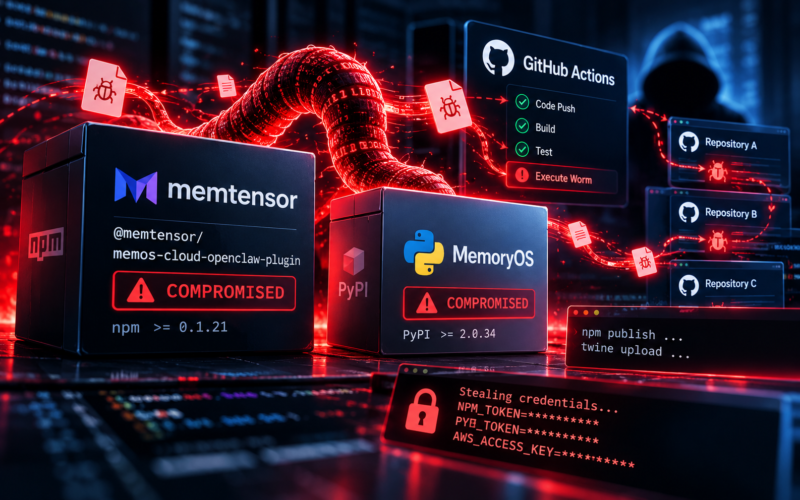
Compromised Memtensor npm plugin spreads worm via GitHub Actions, targets developer credentials

Aikido flags self-propagating malware in trusted packages, with execution shifting from install-time to runtime behavior A compromised npm package linked to Memtensor is being used to distribute a self-propagating supply chain worm capable of spreading across repositories and package registries, according to security firm Aikido. The malware, also identified in a related PyPI package, executes […]

Continue Reading
chosen-brick-spyware

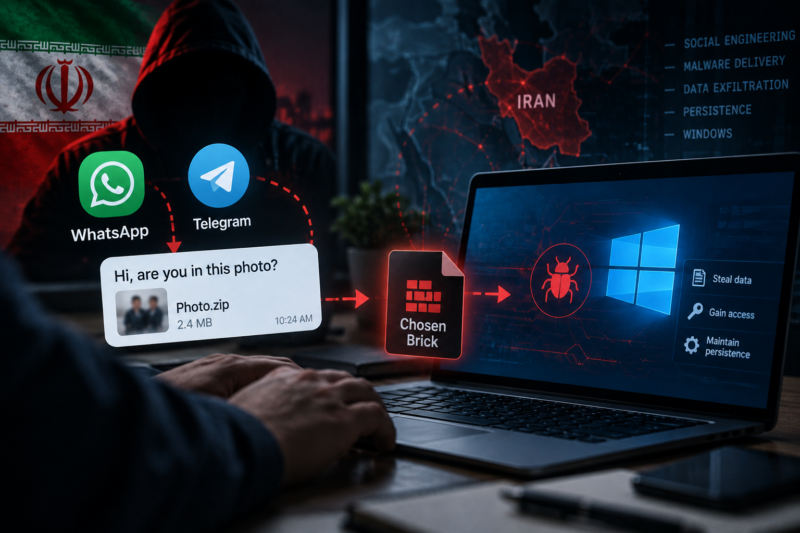
Iranian hackers use Chosen Brick spyware to target Windows systems

FBI, UK NCSC and Dutch AIVD warn Chosen Brick spyware survives reboots and harvests contacts, messages and screen data from compromised systems Iranian state-linked cyber actors are using popular messaging apps to trick targets into installing surveillance malware on their Windows machines, three Western government agencies warned in a joint advisory published Tuesday. The FBI, […]

Continue Reading
mitre-to-pivot-shift

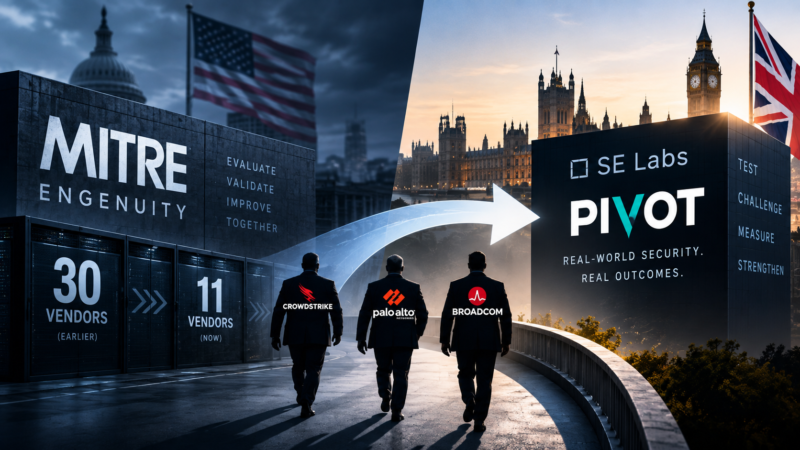
CrowdStrike, Palo Alto Ditch MITRE for UK Rival

Broadcom also joins SE Labs’ new PIVOT programme, as participation in the US-backed MITRE Engenuity evaluations falls from 30 vendors to 11 A wave of major cybersecurity vendors is shifting away from the US Department of Defense-backed MITRE Engenuity ATT&CK Evaluations toward a new independent testing programme run by British company SE Labs, according to […]

Continue Reading